


Managing United States regulations can feel like a never-ending race. Manual spreadsheets often cause errors and missed deadlines. An automated compliance monitoring platform turns static rules into active, real-time insights.
You might wonder how to develop compliance monitoring platform capabilities that truly support your business. The key is a unified system that connects internal controls with external mandates. Centralized evidence collection and testing help teams shift from reactive firefighting toward proactive risk management.
This approach keeps your organization audit-ready each day while reducing staff workload.
Table of Contents
Key Takeaways
- Centralize all regulatory data into one accessible digital hub.
- Automate evidence collection to eliminate manual data entry errors.
- Implement continuous testing to identify risks before they escalate.
- Streamline reporting processes for faster, more accurate audit preparation.
- Foster a culture of accountability across your entire organization.
Define the Compliance Monitoring Goals and Business Scope
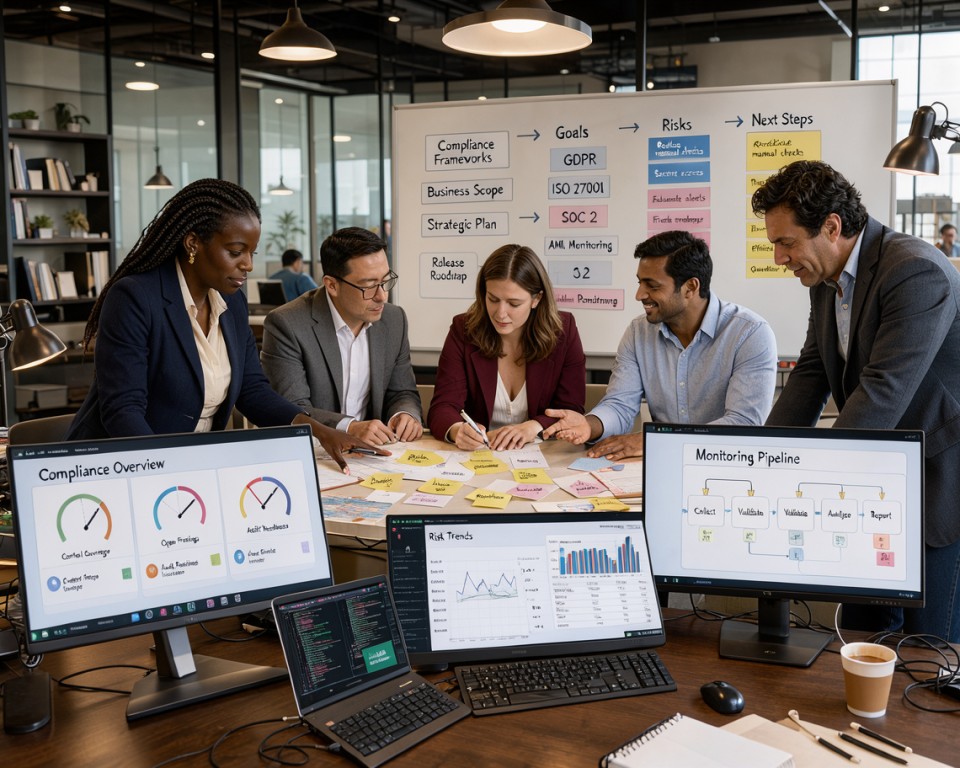
Before writing code, map your compliance goals. Understanding how to develop compliance monitoring platform architectures begins with a clear view of your organization’s needs. Without a roadmap, you may build a system that is too rigid or too broad.
Identify the Regulations, Standards, and Contractual Requirements
First, inventory the rules that govern your business operations. Gather all external mandates requiring consistent oversight and reporting. Group these requirements so you do not miss any critical obligation during design.
- Regulatory mandates: Laws like GDPR, HIPAA, or CCPA that dictate data handling.
- Industry standards: Frameworks such as SOC 2, ISO 27001, or PCI DSS.
- Contractual obligations: Specific security clauses found in customer or vendor agreements.
Effective regulatory compliance monitoring depends on turning complex legal texts into clear technical requirements. Centralizing these documents creates one trusted source for your engineering team.
Set the Platform’s Initial Business Objectives
Your platform should also support internal business goals. You may want to reduce manual audit time or improve your overall security posture. Setting goals early helps you measure your compliance monitoring software as it grows.
Focus on these high-impact areas:
- Reducing the manual effort required for evidence collection.
- Improving the speed of identifying security misconfigurations.
- Increasing transparency for stakeholders and executive leadership.
Choose a Focused Minimum Viable Compliance Scope
It is tempting to automate every control at once, but that choice often causes project fatigue. Start with a Minimum Viable Compliance (MVC) scope that targets your most critical systems. This approach lets you test your regulatory compliance software before expanding it.
Select a pilot scope that includes:
- Systems that store or process sensitive customer data.
- Infrastructure that is subject to the most frequent audit requests.
- Processes where automation provides the highest return on investment.
Starting small lets you improve workflows and build confidence across your organization. This strategic focus delivers immediate value and supports future expansion.
Build a Cross-Functional Compliance and Engineering Team
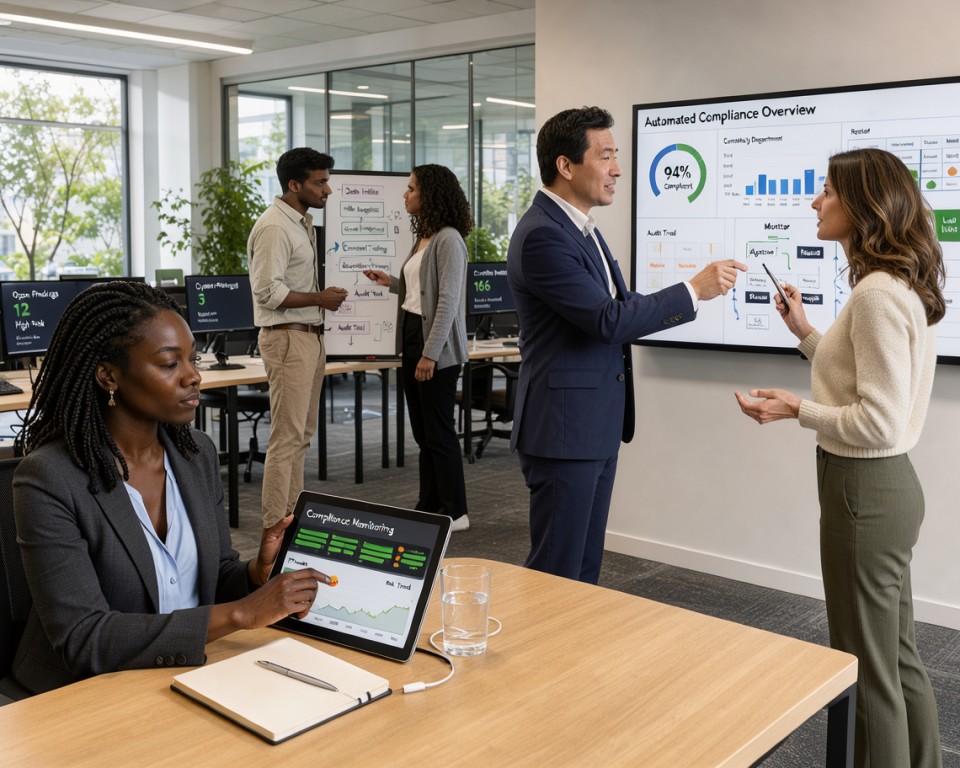
You cannot automate compliance in a vacuum. It requires collaboration across your entire organization. Successful compliance automation depends on breaking down silos between departments that often work independently. Aligning your people ensures technical controls reflect real-world business needs.
Assign Responsibilities Across Legal, Security, IT, and Internal Audit
Each department offers a unique view. Legal teams define regulatory boundaries, while security and IT teams build safeguards that meet those standards. Internal audit provides the necessary oversight to check that controls work as intended.
When these groups work together, they create a shared language for risk. This cooperation makes your compliance management platform a strategic asset, not just a technical tool.
Establish Control Ownership and Approval Authority
Clear accountability supports every effective program. Each control needs a designated owner who manages its upkeep and performance. This person needs the authority to approve changes and sign off on evidence collection processes.
Without clear ownership, tasks can fall through the cracks. Specific roles help team members own their compliance posture. This proactive approach prevents confusion during busy audit cycles.
Document Escalation Paths for Compliance Exceptions
Even the best systems can face unexpected issues or temporary failures. Document clear escalation paths so your team knows what to do when a control fails. This keeps compliance automation moving when technical hurdles arise.
Your compliance management platform should support these workflows by notifying the right stakeholders immediately. When an exception occurs, the system should send the issue to the right manager for review and risk acceptance. Transparency in these processes builds trust with internal leaders and external auditors.
Design the Platform Architecture for Reliable Automation
A strong foundation matters most when you design your automated compliance monitoring platform. A clear architecture keeps the system dependable as your organization grows and its technical environment becomes more complex.
A clean design helps you avoid system downtime and inaccurate data. It also helps your team maintain high standards of integrity across all digital assets.
Separate Data Collection, Assessment, Workflow, and Reporting Services
For reliable performance, separate the core functions of your compliance monitoring software. Separating data collection from assessment keeps incoming log spikes from crashing the evaluation engine.
Each service should run independently in its own environment. This design lets you scale one component, such as reporting, without upgrading the entire infrastructure.
Choose Between a Modular Monolith and Microservices
Your team’s size and requirements should guide the deployment model. A modular monolith suits smaller teams because it simplifies debugging and deployment while keeping code organized.
A microservices architecture gives large-scale regulatory compliance software greater flexibility. It lets teams manage specific services independently and speed up new feature development.
Plan for Availability, Scalability, and Disaster Recovery
Your architecture needs high availability so your automated compliance monitoring platform never misses a critical event. Load balancers and redundant database clusters help maintain uptime during peak traffic.
Disaster recovery is vital for any regulatory compliance software. Test backup and restoration procedures regularly to keep data safe and accessible during unexpected outages.
Use Immutable Logs for High-Value Compliance Events
Mutable data creates a serious risk for high-value events. Using immutable logs ensures unauthorized users cannot alter or delete a compliance record after its creation.
This practice creates an unchangeable audit trail and simplifies work for internal and external auditors. Securing logs strengthens trust in your compliance monitoring software and protects against data tampering.
Map Regulatory Requirements to Measurable Controls
Turn complex regulations into clear steps with measurable control statements. This approach supports effective regulatory compliance monitoring and gives teams live visibility instead of static checklists.
Break Requirements Into Testable Control Statements
Broad regulations often use vague language that auditors cannot test easily. Break these mandates into detailed compliance controls that systems can verify automatically.
Instead of stating “access must be restricted,” define a control like “all administrative accounts must require multi-factor authentication.” This change lets you measure success objectively instead of relying on personal judgment.
“Compliance is not a destination, but a continuous process of aligning technical reality with documented intent.”
Connect Controls to Policies, Assets, Risks, and Owners
A control works best when linked to the right context. Link each technical check to a policy, protected assets, and the compliance risk assessment behind it.
Give each control a clear owner to ensure accountability when testing fails. Engineers should know which policy a failed check violates and which business risk it exposes.
Handle Overlapping Requirements Across Multiple Frameworks
Managing frameworks separately often creates repeated work and wasted resources. Map shared requirements to internal controls and use control testing automation to satisfy several auditors at once.
Map Common Frameworks Such as SOC 2, ISO 27001, HIPAA, and PCI DSS
Many frameworks share goals such as data encryption and access logging. The table shows how one control can meet several regulatory needs at once.
| Control Description | SOC 2 | ISO 27001 | HIPAA | PCI DSS |
|---|---|---|---|---|
| Multi-Factor Authentication | Yes | Yes | Yes | Yes |
| Data Encryption at Rest | Yes | Yes | Yes | Yes |
| Annual Penetration Testing | Yes | Yes | No | Yes |
| Audit Log Retention | Yes | Yes | Yes | Yes |
Efficiency is the main goal of this mapping exercise. By centralizing testing logic, you reduce engineering work while maintaining a high level of security across the entire organization.
Establish a Secure Compliance Data Foundation
A secure data foundation is the most critical step in effective compliance evidence collection. Without a clear view of your digital landscape, consistent oversight across your organization becomes nearly impossible.
Inventory the Data Sources Required for Monitoring
Begin by identifying every location where your organization stores critical information. These locations include cloud environments, endpoint devices, identity management systems, and core business applications.
Creating a complete inventory removes blind spots from your monitoring strategy. Visibility is the first line of defense when building a scalable security compliance platform.

Normalize Evidence From Cloud, Endpoint, Identity, and Business Systems
Raw data often arrives in different formats, making analysis difficult. Normalization transforms these separate logs into one language your system can easily interpret.
Standardizing your inputs helps your compliance controls work reliably across all platforms. This consistency lets your team compare performance metrics without worrying about technical differences underneath.
Apply Data Classification, Retention, and Access Rules
Not all data has the same importance. Classify information by sensitivity so high-risk assets receive the attention they deserve.
Clear retention policies help manage storage costs while meeting regulatory requirements. Proper data governance prevents clutter and keeps audit trails focused on what truly matters.
Protect Sensitive Data With Encryption and Least-Privilege Access
Security must be built into your data foundation from the start. Always use strong encryption to protect sensitive records at rest and in transit.
Furthermore, a least-privilege access model ensures that only authorized personnel can view or modify critical evidence. This approach significantly reduces the risk of accidental exposure or unauthorized tampering within your environment.
Connect the Platform to Systems of Record
Effective automation needs accurate data from the systems your team uses each day. Linking your regulatory compliance software removes manual entry and lowers human error. It builds a living bridge between daily business work and security needs.

Integrate Cloud Platforms and Infrastructure Services
Modern businesses depend on cloud environments such as AWS, Azure, and Google Cloud. These platforms support your digital assets and infrastructure settings. Direct integration gives you real-time insight into your security posture.
This integration lets you monitor storage buckets, network settings, and virtual machine configurations automatically. Your automated compliance checks can flag misconfigurations as soon as they happen, instead of waiting for a quarterly audit.
Connect Identity, Endpoint, Ticketing, and Collaboration Tools
Your compliance plan must cover the tools employees use each day. Identity providers like Okta or Azure AD verify user access and enforce multi-factor authentication. Endpoint management tools also ensure company laptops meet security standards before accessing sensitive data.
Integrating ticketing systems like Jira or ServiceNow helps track remediation efforts. When a control fails, the platform can create a ticket automatically, so no issue is missed. This smooth workflow keeps your team accountable and organized.
Use APIs, Webhooks, and Scheduled Imports Appropriately
Choosing the right data transfer method supports system performance and reliability. APIs exchange data in real time, while webhooks send instant notices for specific events. Scheduled imports often suit high-volume, non-urgent data sets best.
| Method | Best Use Case | Latency |
|---|---|---|
| API | On-demand data retrieval | Low |
| Webhook | Event-driven alerts | Near-zero |
| Scheduled Import | Bulk log analysis | High |
Validate Source Reliability, Permissions, and Synchronization Frequency
Before using incoming data, verify that its source is reliable. Ensure your regulatory compliance software has the minimum necessary permissions to read data without weakening system security. The least-privilege principle protects your organization from possible vulnerabilities.
“Trust is good, but verification is the bedrock of a secure and compliant digital infrastructure.”
Finally, set a clear sync schedule that balances performance with current information. Frequent syncs suit critical security controls, while less frequent updates may work for administrative reporting. Regular validation keeps your automated compliance checks accurate and trustworthy over time.
Automate Evidence Collection and Control Testing
A strong compliance automation strategy replaces static checklists with dynamic, real-time verification. Leaving manual spreadsheets behind gives your organization a clearer view of its security posture. This shift lets your team focus on important security work instead of repeated data gathering.
Define Evidence Requirements for Each Control
Each security control needs a clear definition of valid proof. Identify the data points that show whether a control works as intended. This compliance evidence collection process helps your automated compliance monitoring platform capture the right information from cloud environments and internal systems.
Clear definitions reduce confusion during audits. Mapping logs or configuration states to a control creates a reliable trail of truth. This structure makes it easier to prove that security measures remain active and effective.
Schedule Continuous, Event-Driven, and Periodic Tests
Not every security check needs the same schedule. continuous compliance monitoring tracks high-risk areas in real-time, while other controls may need daily or weekly reviews. Match each testing schedule to the risk profile of its asset.
Event-driven testing adds security by triggering checks after a configuration change. For example, when a new user joins an administrative group, the system can check the change against your policy instantly. This proactive method helps you catch issues before they become major vulnerabilities.
Distinguish Passing, Failing, Inconclusive, and Not-Applicable Results
Standardizing results is vital for effective automated compliance checks. Each test should use a clear category, helping your team prioritize its response. A “Passing” result confirms the control works, while a “Failing” result needs immediate attention.
Sometimes, a test returns an “Inconclusive” result because of missing data or connection issues. Mark controls as “Not-Applicable” when they do not apply to a system or environment. This clarity keeps your team focused on findings that truly matter.
Prevent False Positives With Versioned Test Logic and Exceptions
Managing false positives is a major challenge in control testing automation. If your logic is too strict, you may get unnecessary compliance alerts that distract staff. Versioned test logic lets you update rules without breaking historical data or causing false alarms.
Documented exceptions also help maintain accuracy. When business needs require a temporary policy deviation, record it as an approved exception. Tracking exceptions in your platform keeps automated reports accurate and trustworthy for auditors.
Develop Risk Scoring and Prioritization Rules
A strong compliance risk assessment cuts through endless security alerts. Automated monitoring shows that control failures do not all carry the same weight. A structured approach helps your team address the most critical vulnerabilities first.
Combine Control Results With Asset and Business Context
Monitoring tools provide only a starting point. To make data useful, map each control failure to the assets and business processes it affects. Context is everything when you judge a finding’s true threat level.
For example, a missing patch on a public-facing server matters more than the same issue on an isolated development machine. Linking your asset inventory with your monitoring platform gives you a clearer view of your actual exposure.
Score Likelihood, Impact, Exposure, and Remediation Urgency
A consistent risk scoring framework helps you measure each issue’s severity. Evaluate the likelihood of an exploit and its potential impact on operations. This process assigns a numerical value to every finding.
After scoring an issue, determine its remediation urgency. High-risk items threatening core infrastructure should top your queue. This method keeps staff from becoming overwhelmed by low-priority tasks.
Prioritize Issues That Affect Critical Systems or Regulated Data
Prioritize findings involving sensitive information or mission-critical systems. A control failure exposing customer data or violating specific regulatory requirements needs immediate attention. Focusing your resources there provides the highest return on your security investment.
Allow Reviewers to Override Scores With Documented Justification
Automated systems are powerful, but they sometimes lack the nuance of human experience. Allow authorized reviewers to manually override a calculated risk score when necessary. This flexibility ensures unique business conditions receive proper consideration.
Every override must include a documented justification to maintain an audit trail. This transparency keeps your compliance program accountable while allowing necessary operational adjustments.
Create Remediation Workflows That Drive Accountability
A strong compliance management platform does more than find gaps. It turns raw data into clear tasks, so each security finding gets proper attention. This approach changes passive monitoring into an active compliance remediation workflow that helps keep your business secure.
Route Findings to the Correct Owner and Team
Effective remediation starts by assigning each task to the right person. When a control fails, the system should use your internal directory to find the asset owner or responsible department. This removes confusion and immediately alerts the team best equipped to fix the issue.
- Automated assignment based on asset ownership.
- Notification triggers for team leads and managers.
- Clear documentation of who is responsible for the fix.
Set Due Dates Based on Severity and Regulatory Expectations
Not every finding needs an immediate response, but teams must address critical risks without delay. Matching due dates to regulatory requirements shows auditors that your organization takes compliance seriously. The table below shows a standard way to prioritize remediation efforts.
| Severity Level | Regulatory Priority | Standard Due Date |
|---|---|---|
| Critical | Immediate | 24 – 48 Hours |
| High | Urgent | 15 Days |
| Medium | Moderate | 30 – 60 Days |
Track Exceptions, Compensating Controls, and Risk Acceptance
A direct fix may not be possible because of technical limits or business needs. In these cases, your compliance management platform must support formal exception processes. Document compensating controls that reduce the risk, and ensure leaders formally accept the remaining exposure.
A clear audit trail for these decisions is vital. Tracking every exception gives auditors a transparent view of why some controls remain non-compliant. This detail helps maintain trust and operational integrity.
Connect Findings to Jira, ServiceNow, and Other Ticketing Systems
To streamline your compliance remediation workflow, integrate your platform with tools engineers already use. Linking findings to systems such as Jira or ServiceNow lets teams manage compliance tasks with their daily development work. This keeps security requirements visible throughout the standard project management lifecycle instead of isolating them.
Design Alerts Without Creating Compliance Noise
Smart notification design turns raw data into a clear compliance remediation workflow. With continuous compliance monitoring, your goal is useful guidance, not endless notifications. Filtering background noise helps your team focus on issues that matter to the organization.
Define Thresholds for Immediate, Daily, and Periodic Notifications
Not every finding needs an instant response. Sort your compliance alerts by risk, urgency, and possible impact. Send immediate notifications for critical failures that threaten security or regulatory standing.
Send daily summaries for non-critical issues needing attention during a standard business cycle. Periodic reports give management a high-level view of trends and overall environment health without tracking every minor event.
Use Deduplication and Alert Grouping for Related Findings
One misconfiguration can trigger dozens of alerts across different systems. Your platform needs deduplication logic to find findings with the same root cause. Grouping related items into one ticket or notification saves engineer time and reduces frustration.
Deliver Alerts Through Email, Slack, Microsoft Teams, and Ticket Queues
Good communication meets your team where it already works. Route high-priority items to ticketing systems like Jira or ServiceNow, so they enter the standard compliance remediation workflow. For less urgent updates, use Slack or Microsoft Teams to inform stakeholders without filling primary email inboxes.
Measure Alert Quality Through Response and Resolution Trends
Review your notification strategy often by tracking key performance indicators. Measure how quickly teams acknowledge and resolve issues found by your continuous compliance monitoring system. A high volume of ignored alerts shows that you should refine thresholds and improve signal quality.
Build Audit-Ready Evidence and Reporting
True regulatory compliance monitoring needs more than log collection. It needs a clear chain of custody for each piece of evidence. Connected systems create a reliable path that proves your security posture is real and verifiable.
Maintain Evidence Chains From Source Data to Control Result
An effective automated compliance monitoring platform must capture each data point’s full lifecycle. Linking raw system logs to control requirements ensures every finding has irrefutable proof.
This traceability shows your team why a control passed or failed. It removes guesswork from manual reviews and gives external reviewers a clear narrative.
Generate Reports for Executives, Control Owners, and Auditors
Stakeholders need different details to make informed decisions. A high-level compliance dashboard gives executives the big picture, while detailed reports give control owners data to fix issues.
“Compliance is not a destination, but a continuous journey of transparency and improvement.”
Tailored output keeps everyone informed without irrelevant technical noise. This focused approach is a hallmark of modern audit compliance tools.
Preserve Timestamps, Approvals, Changes, and Evidence History
A permanent record of system changes supports long-term accountability. Your platform should log who approved each change, when it occurred, and what the previous state was.
This history matters during an audit. It shows that your organization maintains rigorous control over its environment at all times.
Support Common Audit Requests Without Manual Spreadsheet Assembly
You should no longer spend weeks gathering audit documents by hand. With audit-ready reporting, you can export complete evidence packages in a few clicks.
| Feature | Manual Process | Automated Platform |
|---|---|---|
| Evidence Gathering | Days of work | Real-time access |
| Data Accuracy | Prone to error | High integrity |
| Audit Readiness | Reactive | Always prepared |
Streamlining compliance evidence collection saves valuable team time and lowers human error risk. Organized, accessible data lets you improve security instead of chasing spreadsheets.
Create Dashboards for Different Compliance Stakeholders
Modern audit compliance tools must meet the needs of executives, managers, and auditors. A well-designed compliance dashboard serves as the central nervous system for your regulatory program. It shows each person useful data and keeps everyone aligned with organizational goals.
Show Executives Organization-Wide Risk and Compliance Trends
Executives need a high-level view of the company’s overall risk posture. They need to see how well the organization meets its regulatory obligations without technical jargon. A robust compliance management platform gives leaders clear trend lines and heat maps that show areas of concern.
These visual reports help leaders make informed choices about resources and risk appetite. Tracking progress over time helps executives spot better security or emerging gaps. This transparency helps maintain trust with board members and external stakeholders.
Give Control Owners Actionable Work Queues
Control owners need more than charts; they need actionable insights for daily tasks. Effective compliance monitoring software gives them personalized work queues. These queues prioritize pending evidence requests and remediation items, removing guesswork from compliance management.
When a control owner logs in, the system should show what needs attention. Grouping tasks by severity and due date helps teams address critical issues first. This streamlined workflow reduces the administrative burden on IT and security staff.
Provide Auditors With Scope, Evidence, and Testing Details
Auditors need a close look at your control environment. They must verify sound testing methods and accurate, complete evidence. A professional compliance dashboard packages this information and simplifies the audit process.
Direct access to testing logs, policy mappings, and historical evidence saves time during assessments. When auditors trace control results to their sources, they gain confidence in internal processes. This transparency turns a stressful audit into a smooth, collaborative experience.
Use Drill-Down Views Instead of Overloaded Summary Screens
Avoid cramming every metric onto one screen. Use drill-down views so users can start with a summary and open details as needed. This design keeps the interface clean while making deeper data accessible.
| Stakeholder | Primary Focus | Key Dashboard Feature |
|---|---|---|
| Executives | Risk Trends | High-level heat maps |
| Control Owners | Task Completion | Actionable work queues |
| Auditors | Evidence Integrity | Detailed audit trails |
Secure the Platform and Protect Its Integrity
Treat your security compliance platform as carefully as your most sensitive production systems. If attackers compromise its foundation, the entire audit trail becomes unreliable. Protecting system integrity keeps your compliance controls effective and trustworthy over time.
Implement Role-Based Access and Segregation of Duties
Effective security begins with least privilege. Assign permissions only by job function to block unauthorized access to sensitive data.
Segregation of duties also protects platform integrity. Do not let one user configure a control and approve its results. This check-and-balance system helps prevent internal fraud.
Protect Credentials, Tokens, and Integration Secrets
Your platform may connect to cloud services and databases through API keys or service tokens. Never store these secrets in plain text; doing so creates a serious security risk.
Use a dedicated secrets management service to encrypt and rotate these credentials automatically. If someone exposes a configuration file, this practice still helps keep your underlying security compliance platform secure.
Audit Administrative Actions and Configuration Changes
Log every system setting change in an immutable audit trail. Record changes to user roles, alert thresholds, and the underlying logic of your compliance controls.
Review these logs often to spot suspicious behavior early. They also give external auditors evidence that your platform has not been tampered with during the reporting period.
Test for Injection, Broken Access Control, and Evidence Tampering
Proactive testing provides the final defense layer for your infrastructure. Run regular vulnerability scans to find injection flaws that could let attackers manipulate your data.
Also, conduct penetration tests focused on broken access control. Verify that users cannot view or modify evidence outside their assigned scope. This protection is essential for preserving your compliance program’s integrity.
| Security Feature | Primary Benefit | Implementation Priority |
|---|---|---|
| Role-Based Access | Limits user exposure | High |
| Secret Management | Prevents credential theft | High |
| Audit Logging | Ensures accountability | Medium |
| Injection Testing | Hardens system code | High |
Test the Platform Before Organization-Wide Deployment
You cannot trust automated systems until they face real-world scenarios. Before you deploy them company-wide, perform a thorough compliance risk assessment to ensure your tools behave as expected. This phase catches errors before they affect production.
Validate Control Logic Against Known Compliant and Noncompliant Cases
Start by creating test cases that represent both perfect compliance and known failures. Feed these scenarios into your automated compliance checks to verify that the system flags issues correctly. Precision is key here, because alerts should appear only after genuine violations.
Run Integration, Load, Security, and Failure-Recovery Tests
Your platform must handle the demands of a live enterprise environment. Integration tests ensure data flows smoothly between cloud services and the monitoring engine. Simulate high-load conditions to see whether the system stays responsive during peak activity.
Do not forget to test your security posture and recovery capabilities. If a service goes down, your platform should restart and resume monitoring without losing critical evidence. Resilience is a core requirement for any tool that tracks your organization’s security posture.
Compare Automated Results With Manual Compliance Reviews
Build trust in your new system by running it beside manual audits. Have your team review one specific system manually, then compare those findings with your risk scoring framework output. If the results align, you can move forward with confidence.
Measure Accuracy, Coverage, Processing Time, and False-Positive Rates
To truly master control testing automation, track specific performance metrics. These metrics show whether your platform helps or adds noise to daily operations.
- Accuracy: Does the system correctly identify the state of the control?
- Coverage: Are all critical assets included in the monitoring scope?
- Processing Time: How long does it take to generate a report after a change?
- False-Positive Rates: How often does the system flag a compliant item as a failure?
By keeping these metrics low and manageable, you help your team focus on real risks instead of chasing ghosts. Continuous improvement based on these measurements will keep your compliance posture strong and reliable over time.
Roll Out the Platform and Improve It Continuously
Launching your automated compliance monitoring platform starts a safer, more efficient operation. Moving from controlled development to live production turns your framework into a useful daily asset. This shift requires steady leadership and focus on long-term stability.
Launch a Pilot With High-Value Systems and Cooperative Owners
Start with a small, high-value group of systems for your first pilot. Work with cooperative control owners to gather honest feedback and find friction points. These early adopters can refine your compliance automation logic before you expand across the organization.
Critical assets keep your most important data protected while you test system reliability. This focused approach shows stakeholders immediate value. It also builds trust in your new continuous compliance monitoring capabilities.
Train Users on Findings, Exceptions, Evidence, and Escalations
Once the pilot starts, train every involved team member. Users must interpret findings and use the compliance remediation workflow effectively. Clear guidance for documenting exceptions and supplying evidence prevents confusion and reduces manual work.
Set clear escalation paths so team members know whom to contact about critical issues. Confident users are more likely to manage alerts and engage with the system. Consistent training connects complex technology with a user-friendly compliance culture.
Expand Coverage in Controlled Releases
After a successful pilot, expand coverage through controlled, incremental releases. This plan lets you track how compliance automation affects system performance and team capacity. Staged rollouts help you solve problems without overwhelming your staff.
Treat each release as a chance to improve your continuous compliance monitoring processes. Use data from each phase to refine integrations and improve alert accuracy. This process keeps your platform reliable during security work.
Review Metrics and Retire Controls That No Longer Reflect Risk
An effective automated compliance monitoring platform needs regular control library maintenance. Review performance metrics to find controls that provide useful insights or create noise. Retire requirements that no longer match your current risk profile.
Streamlining controls keeps your compliance remediation workflow focused on business priorities. Removing outdated or repeated checks keeps your team focused on high-priority risks. Continuous improvement keeps your compliance posture strong as the digital landscape changes.
Conclusion
Strong regulatory oversight means replacing manual checklists with dynamic, automated systems. Learning how to develop compliance monitoring platform capabilities helps your team find risks before they affect business operations.
Modern organizations use reliable audit compliance tools to track their security posture. Adding these tools to daily workflows helps keep every control effective and transparent. This proactive approach turns compliance from a burden into a strategic advantage.
Reliable data supports a strong compliance strategy. Accurate evidence collection enables audit-ready reporting for even the most rigorous external reviews. This precision builds stakeholder trust and gives leaders insights for informed decisions.
Begin automated oversight with small, intentional steps. Identify critical assets and map them to primary regulatory requirements. Improving internal processes consistently keeps your organization resilient in a changing digital landscape.