


Modern digital work depends on smooth connections among customers, partners, and core systems. These interfaces connect your organization, making API security development vital for every technical team.
Without proper safeguards, these pathways attract malicious actors. Strong business application security keeps your data private and services available to those who need them most.
A strong defense combines identity controls, validation, and constant monitoring. Add these practices early to reduce exposure and build stronger infrastructure for the future.
Table of Contents
Key Takeaways
- Understand how digital interfaces serve as the backbone for modern enterprise connectivity.
- Learn why proactive protection is essential to prevent unauthorized access to sensitive data.
- Discover how identity management and validation reduce your overall risk profile.
- Explore the importance of continuous monitoring in identifying potential threats in real-time.
- Gain actionable insights to strengthen your team’s approach to technical defense strategies.
Why API Security Development Matters for Modern Business Applications
Today, APIs connect core systems with the outside world and move data between them. They drive innovation but also widen your organization’s attack surface. Prioritizing API security is now essential for business application security, not merely a technical task.
How APIs Connect Customers, Employees, Partners, and Core Systems
APIs act as digital glue that holds modern enterprises together. They let mobile apps reach backend databases, help partners use your services, and give employees smooth access to internal tools. This high level of connectivity improves efficiency but creates many entry points needing constant attention.
Why APIs Expose Sensitive Data and High-Value Business Functions
Because APIs must perform tasks, they often provide direct access to high-value assets. An API might expose customer records, payment processing workflows, or proprietary internal logic. If endpoints lack proper security, attackers can exploit them, bypass traditional perimeter defenses, and access sensitive information directly.
The Business Impact of API Attacks
A compromised API can harm the entire organization, not just the IT department. One vulnerability can trigger many problems and threaten organizational stability.
Financial losses, operational disruption, and regulatory penalties
Security breaches often create immediate financial strain. Companies may face heavy fines for failing to protect user data under regulations like GDPR or CCPA. Downtime needed to fix an attack can also stop revenue-generating work for days or even weeks.
Reputational damage and loss of customer trust
Trust is the most valuable currency in the digital economy. After a data leak, rebuilding customer confidence becomes an uphill battle. Maintaining robust business application security helps protect your reputation and support long-term growth.
| Impact Category | Primary Consequence | Business Risk Level |
|---|---|---|
| Financial | Direct theft and regulatory fines | Critical |
| Operational | System downtime and service outages | High |
| Reputational | Loss of customer loyalty and brand value | High |
Common API Attacks That Threaten Business Applications
Even well-designed applications can face sophisticated API attacks when developers overlook common weaknesses. These pathways support modern business, but attackers target them to reach sensitive information without permission.
Broken object-level authorization and unauthorized data access
This weakness appears when an API does not check whether a user may access a specific object. Attackers can change IDs in URLs to view other users’ data. Proper authorization checks ensure users interact only with their own records.
Broken authentication and stolen credentials
Weak authentication lets attackers steal tokens or passwords. With valid credentials, they can impersonate users or administrators. Using multi-factor authentication and secure token management helps stop these API attacks.
Excessive data exposure and mass assignment
Some developers let clients filter data, which creates risk. APIs may return complete objects, exposing sensitive fields that should stay hidden. Mass assignment happens when an API binds user input to internal properties without proper validation.
Injection attacks, including SQL and command injection
These attacks begin when an API treats untrusted data as part of a command or query. Malicious code can change backend databases or run unauthorized system commands. Strict input validation and parameterized queries provide the best defense against these threats.
Denial-of-service attacks and unrestricted resource consumption
Attackers may flood an API with requests until server resources run out. This can cause outages that affect customers and business operations. Setting rate limits and quotas helps prevent one user from controlling your infrastructure.
Server-side request forgery and malicious third-party integrations
SSRF happens when an attacker forces an API to contact private internal systems. Untrusted third-party integrations can also create hidden risks. Always check external data before using it in your business logic.
| Attack Type | Primary Risk | Defense Strategy |
|---|---|---|
| BOLA | Unauthorized Data Access | Object-level checks |
| Injection | System Compromise | Input sanitization |
| DoS | Service Downtime | Rate limiting |
| Credential Theft | Account Takeover | Strong authentication |
Build Security Into the API Development Lifecycle
Building security into the API security development lifecycle is an effective way to prevent vulnerabilities before production. Finding risks early helps teams avoid the high costs and stress of emergency patches.
Making security a final release gate can cause bottlenecks and leave flaws unseen. Instead, make security part of every development phase.
Define security requirements before writing API code
Before coding starts, your team must set clear security expectations. Define who may access each endpoint and what level of authentication each function requires.
Early documentation helps developers understand their security duties. It makes security a foundational element of the application architecture, not an afterthought.
Model threats across endpoints, data flows, and trust boundaries
Threat modeling shows how data moves through your system. Review endpoints and trust boundaries to find services giving untrusted callers too much access.
This proactive approach to API security development reveals hidden risks in complex integrations. It makes developers ask how data is handled and where it could be exposed.
Use secure coding standards during implementation
Industry-standard coding practices help reduce common vulnerabilities. Developers should choose libraries and frameworks with built-in protection against injection attacks and other common threats.
Consistent coding standards make the codebase easier to maintain. When everyone follows the same rules, teams can spot changes that may create security gaps.
Review security controls during code review
Code reviews should include a specific check for security controls. Peer reviews can catch logic errors that automated tools might miss.
Check that authorization works correctly at the object level. Confirming proper handling of sensitive data is a critical step in maintaining a secure environment.
Carry security checks from development through production
Security expectations must stay consistent in development, staging, and production. A less secure testing environment can let untested vulnerabilities reach production.
Continuous security checks help defenses grow with your application. This vigilance protects your business from emerging threats and keeps your API security development process efficient and reliable.
Design a Secure API Architecture
A secure API architecture forms the foundation for every other security control. Intentional design choices can greatly reduce the size and accessibility of your API attack surface. This proactive approach helps business applications stay resilient against changing threats.
Separate public, partner, internal, and administrative APIs
Not all APIs serve the same purpose or need the same exposure level. Isolate endpoints by intended audience to help prevent attackers from moving across systems.
- Public APIs: Designed for open consumption with strict rate limiting.
- Partner APIs: Restricted to specific business entities with verified credentials.
- Internal APIs: Hidden from the public internet to support core business logic.
- Administrative APIs: Highly sensitive interfaces requiring multi-factor authentication.
Choose REST, GraphQL, or gRPC with security considerations in mind
Each protocol brings benefits, but each also creates different security risks. REST is widely understood, while GraphQL offers flexibility that can cause excessive data exposure without careful controls. gRPC delivers high performance but needs careful handling of binary payloads and authentication headers.
Use API gateways to centralize traffic controls
An API gateway serves as a critical enforcement point for your infrastructure. It lets you manage authentication, logging, and traffic shaping from one location. Centralized controls help apply consistent security policies across your services.
Apply zero-trust principles between services
Never assume a request is safe because it comes from inside your network. A zero-trust model verifies every request, regardless of its source. This approach stops attackers from using internal trust to move through your systems.
“The perimeter is no longer a wall; it is a series of identity-based checkpoints that must be verified at every turn.”
Limit trust in client applications and downstream systems
Client applications and downstream systems should not receive automatic trust because they join an approved workflow. Validate inputs and verify permissions at every process step. This defense-in-depth strategy helps prevent one compromise from causing total system failure.
Protect service-to-service communication with mutual TLS
Mutual TLS (mTLS) makes both the client and server verify each other’s identity. It creates an encrypted tunnel that blocks unauthorized entities from intercepting or spoofing internal traffic.
Use network segmentation and private endpoints where appropriate
Private endpoints keep API traffic completely off the public internet. Network segmentation further limits a breach’s blast radius by isolating sensitive services from less secure components. These measures are essential for maintaining a truly secure API architecture.
Strengthen Authentication and Authorization Controls
Protecting digital infrastructure requires a clear difference between identity checks and permission decisions. API authentication confirms who makes a request, while API authorization controls what that user or service may do. Balancing both controls helps maintain a secure environment.
Select the right authentication method for each API consumer
OAuth 2.0 and OpenID Connect for delegated access
For applications with user interaction, OAuth 2.0 and OpenID Connect offer a standard framework for delegated access. Users can grant third-party applications access to resources without sharing their primary credentials. This approach lowers the risk of exposed credentials across your ecosystem.
Short-lived tokens, refresh tokens, and secure token storage
Security teams should use short-lived access tokens to reduce attackers’ opportunity. When a token expires, a secure refresh token obtains a new one without requiring user reauthentication. Store these tokens in secure, encrypted environments to prevent unauthorized interception.
API keys for controlled machine-to-machine identification
When services communicate directly without a user, API keys provide a simple identification method. Treat these keys as sensitive secrets. Always rotate them regularly and limit their scope to functions required for machine-to-machine interaction.
Enforce authorization at the object and function levels
Authentication is only the first step in a complete security strategy. Verify that each authenticated caller has permission to access specific objects or perform sensitive functions. Perimeter security alone can leave internal data vulnerable to exploitation.
Use role-based and attribute-based access control appropriately
Role-Based Access Control (RBAC) assigns permissions according to user job functions. For finer control, Attribute-Based Access Control (ABAC) checks factors such as time, location, or resource sensitivity. Together, these methods keep access least-privileged and aware of context.
Prevent privilege escalation and insecure direct object references
Attackers may change parameters to access other users’ data, creating a flaw called Insecure Direct Object Reference (IDOR). Validate that the requester owns the resource before returning data. Also, prevent users from raising their privileges by changing request payloads or headers.
Manage credentials, secrets, and token revocation securely
Hardcoding secrets in source code creates a serious security risk. Use dedicated secret management services to store and inject credentials at runtime. Maintain strong token revocation so you can immediately invalidate access after detecting a compromise.
Protect API Data With Validation, Encryption, and Minimization
Strong cybersecurity starts with protecting sensitive information across your API ecosystem. Secure how data moves, stays stored, and gets handled. Effective API data protection uses strict validation and strong encryption together.
Validate request parameters, headers, payloads, and content types
Treat every incoming request as potentially harmful. Check each input’s format, length, and type before processing it. This step helps stop attackers from injecting harmful code into backend systems.
Use allowlists and strict schemas instead of permissive parsing
Permissive parsing can allow unexpected data structures to enter your system. Instead, define strict schemas that clearly state what your API accepts. Allowlists permit only known, safe inputs to reach your business logic.
“Security is not a product, but a process. By enforcing strict data validation, you transform your API from a vulnerable entry point into a hardened asset.”
Encrypt data in transit with modern TLS configurations
Data moving between clients and servers can be intercepted. Use TLS encryption to protect its confidentiality. Choose modern protocols and strong cipher suites to keep network traffic secure.
Protect sensitive data at rest and in application logs
Encryption must continue beyond the network edge. Protect sensitive information in databases and temporary files. Never store raw passwords, tokens, or personal identifiers in plain-text application logs.
Return only the data each caller needs
Returning full database objects can expose more information than needed. This practice, called over-fetching, reveals unnecessary internal data. Filter each response so callers receive only what their tasks require.
Mask personal, financial, health, and authentication information
Use masking when sensitive data must appear on screen. For example, show only the last four credit card digits or part of an email address. These methods support API data protection and help protect your users’ privacy.
- Validate: Check all headers and payloads against strict rules.
- Encrypt: Use modern TLS for all data in transit.
- Minimize: Send only the data required for the specific request.
- Mask: Obfuscate sensitive fields like PII and financial records.
Control API Traffic and Prevent Abuse
Effective API traffic control shields systems from accidental overloads and malicious activity. Managing incoming requests keeps services available for legitimate users. A strong strategy for API abuse prevention helps maintain a healthy digital ecosystem.
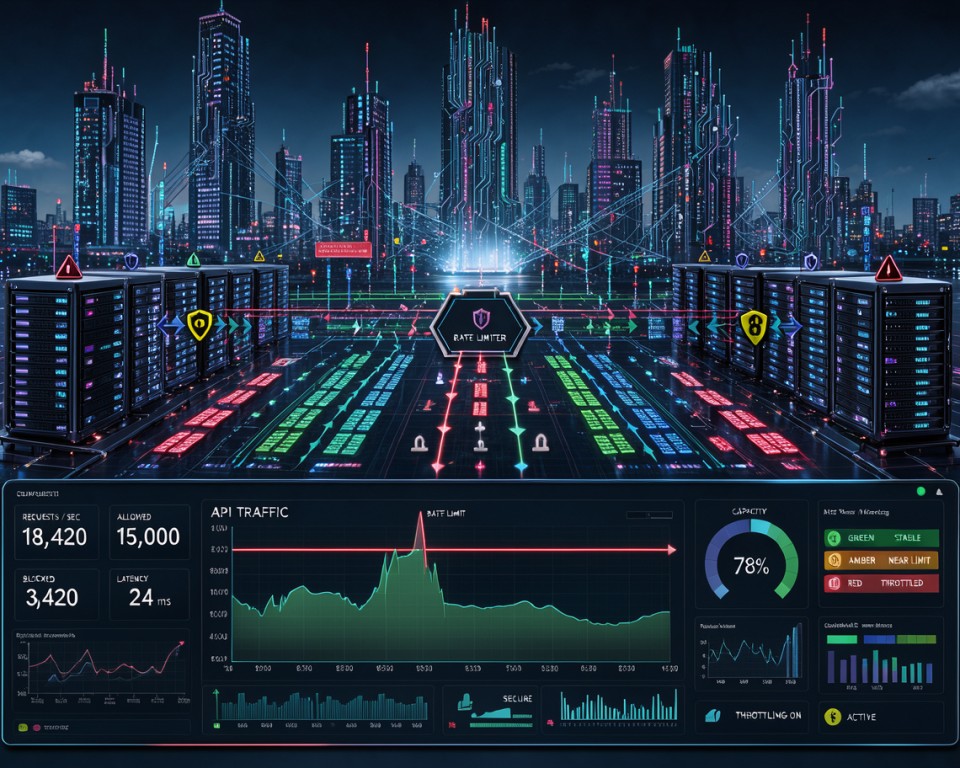
Set rate limits by user, token, IP address, and endpoint
Use API rate limiting to stop one source from overwhelming your infrastructure. Track requests by token or IP address to enforce fair usage policies. This prevents one user or automated script from taking all server resources.
Use quotas and throttling to protect expensive operations
Some API calls, including complex database queries and heavy report generation, use far more resources. Apply quotas to limit how often these expensive operations run. Throttling these endpoints helps keep systems stable during high demand.
Apply request-size limits and timeout controls
Attackers may crash services with huge payloads or connections held open indefinitely. Set strict limits on incoming request sizes to prevent memory exhaustion. Also, use short timeouts so stalled connections do not consume worker threads.
Defend against credential stuffing and automated attacks
Automated bots often target login endpoints with stolen credentials. Behavioral analysis and CAPTCHA challenges can reduce risks when suspicious patterns appear. Protecting authentication is vital to a complete API abuse prevention strategy.
Use pagination, caching, and asynchronous processing safely
Large responses can slow performance for everyone. Use pagination to split results into smaller chunks and reduce backend load. Cache frequent responses and send heavy tasks to asynchronous workers to keep the primary API responsive.
Distinguish normal traffic from abusive behavior
Separate normal user surges from malicious attacks. Monitor traffic patterns for unusual request frequency or unexpected geographic spikes. Effective API rate limiting requires this visibility, so loyal customers remain unblocked during peak hours.
Secure Third-Party APIs, Webhooks, and Integrations
Your application is only as secure as its weakest external connection. External services can improve productivity, but they also greatly expand your attack surface. Strong third-party API security helps protect your data from outside threats.
Assess vendor security before granting API access
Before connecting a new service, complete a thorough security review. Assess how the vendor handles data, responds to incidents, and controls internal access. Trusting a partner blindly is a common mistake that can cause major data breaches.
Restrict integration permissions to the minimum required scope
Follow the principle of least privilege when setting up API keys or OAuth tokens. Grant only the permissions the integration needs to work. If a service only reads data, never give it write or delete access.
Verify webhook signatures and protect callback endpoints
Effective webhook security depends on confirming incoming data comes from your trusted provider. Always validate digital signatures on webhook payloads to ensure attackers have not changed them. Authentication for callback endpoints also helps prevent unauthorized access.
Prevent replay attacks with timestamps and unique request identifiers
Attackers may capture and resend valid requests to trigger duplicate actions. Prevent replay attacks by adding timestamps and unique request identifiers to communication protocols. Your system should automatically reject requests with expired timestamps or reused IDs.
Validate external responses before using them in business logic
Never assume data from an external source is clean or safe. Treat all third-party API responses as untrusted input, and validate them against strict schemas. This practice keeps malicious payloads from harming internal business logic or database integrity.
Monitor vendor changes, outages, and compromised credentials
Security is an ongoing process, not a one-time setup. Monitor vendors for service outages, API version changes, and reports of compromised credentials. Staying informed helps your team respond quickly when a partner’s security posture changes unexpectedly.
Test APIs for Vulnerabilities Before Release
A layered testing strategy finds and fixes vulnerabilities in your digital infrastructure. Early fixes protect users and preserve the integrity of your business systems.
Combine automated scanning with manual security testing
Relying on one method rarely catches every flaw. You should combine automated tools with human expertise for broad coverage. Machines find known patterns, but manual API security testing uncovers complex logic errors scanners often miss.
Test authentication, authorization, and tenant isolation
Your checks must confirm users access only information they are permitted to see. Test for broken access controls and ensure users cannot view private data belonging to others. In multi-tenant environments, Tenant isolation prevents cross-account data leaks.
Use schema validation and contract testing in CI/CD pipelines
Adding API vulnerability scanning to development helps stop insecure code from reaching production. Strict schema validation ensures the system processes only expected data formats. Contract testing keeps services consistent and reduces unexpected behavior during integration.
Perform fuzz testing against parameters and request bodies
Fuzz testing sends malformed or unexpected data to endpoints and observes their responses. It can uncover hidden crashes and memory leaks. Robust error handling helps systems fail safely without exposing sensitive information.
Test for injection, data leakage, and business-logic flaws
Look beyond standard checks for SQL injection and command injection. Audit responses to ensure they do not reveal sensitive details. Business-logic testing confirms intended workflows and prevents application manipulation for unauthorized gain.
Use realistic test data without exposing production information
Real data can help testing, but never use actual customer records. Create synthetic datasets that mimic the complexity of production traffic instead. This validates security controls without risking user privacy.
Integrate SAST, DAST, dependency scanning, and secret detection
Automated tools should support your daily security routine. Static analysis (SAST) and dynamic analysis (DAST) provide a security baseline, while dependency scanning finds flaws in third-party libraries. Always use secret detection to prevent API keys or passwords from entering your code repository by mistake.
Prioritize remediation by exploitability and business impact
Not every vulnerability has the same importance. Rank findings by how easily attackers can exploit them and their potential business damage. Prioritizing high-impact risks helps your team focus time where it matters most.
Monitor API Activity and Detect Attacks
You cannot protect what you cannot see, so constant oversight is essential. Robust API monitoring provides the visibility needed to spot threats in real time. It turns raw traffic data into useful intelligence, helping your team stay ahead of attackers.
Capture useful security events without logging sensitive data
Effective logging balances security and privacy. Focus on metadata, such as request timestamps, source IPs, and response codes. Always avoid storing sensitive information such as passwords, credit card numbers, or personal health data in your logs.
Track authentication failures, authorization denials, and unusual access
Monitoring failed login attempts is a critical first step in spotting brute-force attacks. Also watch for authorization denials, which may signal probing for restricted data. Tracking these patterns helps you spot malicious actors before they gain a foothold.
Monitor changes in traffic volume, geography, and client behavior
Sudden traffic spikes can signal a denial-of-service attack or a misconfigured client. Also monitor the geographic origin of your requests. If traffic suddenly surges from a region where you have no customers, investigate.
Connect API telemetry to SIEM and detection systems
Centralized security data is more powerful. Feed telemetry into a Security Information and Event Management (SIEM) system to connect events across your entire stack. This integration supports faster incident response and deeper forensic analysis.
Create alerts for high-risk endpoint and account activity
Not every event needs an immediate response, but high-risk actions do. Set automated alerts for suspicious activity, such as repeated access to sensitive endpoints or rapid credential changes. These notifications help your team act quickly when it matters most.
Use dashboards to measure security and reliability together
Security should never exist in a vacuum. Unified dashboards let you track both performance metrics and security health at once. This broad view helps ensure your API monitoring efforts do not harm the user experience or system speed.
Prepare an API Incident Response and Recovery Plan
When digital infrastructure faces a sudden threat, a clear recovery roadmap helps protect your systems. A strong API incident response plan helps your team act quickly and limit damage. Preparing early reduces the pressure and uncertainty that often follow API attacks.
Define ownership for API security incidents
Clear communication begins with clear ownership. Designate an incident response team with security engineers, developers, and legal counsel. Give this team authority to make high-stakes decisions during an active event.
Contain attacks by revoking tokens, blocking clients, and isolating services
Act quickly when you detect malicious activity. Contain API attacks by revoking compromised access tokens or blocking specific IP addresses. For a severe breach, isolate the affected service from the rest of your network.
Investigate affected endpoints, accounts, records, and time periods
After containing the threat, determine the incident’s full scope. Review logs to find accessed endpoints and compromised user accounts. This work reveals the timeline and data that may have been exposed.
Preserve logs and evidence for legal and compliance needs
Keep a clean audit trail for internal reviews and external requirements. Back up relevant logs and store them in a secure, immutable location. This evidence supports reports to authorities or insurance providers.
Notify customers, partners, and regulators when required
Transparency builds lasting trust with stakeholders. If sensitive data is involved, follow legal guidelines and notify affected parties promptly. Clear, honest communication helps protect your brand’s reputation.
Recover safely and turn incident lessons into engineering improvements
Recovery means more than bringing systems back online. Use investigation data to patch vulnerabilities and update security protocols. These engineering improvements strengthen defenses against future API incident response challenges.
| Incident Phase | Primary Action | Key Goal |
|---|---|---|
| Preparation | Define roles and teams | Reduce response time |
| Containment | Revoke tokens and block IPs | Stop the data breach |
| Investigation | Analyze logs and endpoints | Determine the scope |
| Recovery | Patch and improve code | Prevent future recurrence |
Govern API Security Across Teams and Environments
Effective API governance supports consistent security standards across your organization. As your digital footprint grows, tracking every connection point becomes vital for long-term success. A unified approach helps teams move quickly while controlling risk.
Maintain an accurate inventory of APIs and their owners
You cannot protect what you do not know exists. A complete inventory should list every API, its owner, version, and current exposure level. This view helps teams find undocumented endpoints that often become hidden targets for attackers.
Apply consistent policies across development, staging, and production
Security should not change when code moves from a laptop to the cloud. Uniform policies keep API security controls effective throughout the software lifecycle. This consistency limits configuration drift and lowers the risk of human error.
Manage API versions, deprecation, and undocumented endpoints
Old, unmaintained APIs often give malicious actors an easy entry point. A clear policy for versioning and deprecation is essential. Regular audits help identify and retire legacy services that no longer support business goals.
Use security standards such as OWASP API Security Top 10
The OWASP API Security Top 10 gives your staff a shared vocabulary. This framework helps developers, product managers, and operations teams discuss risks in common language. It serves as a foundational guide for prioritizing security reviews and technical discussions.
Train developers, product teams, and operations staff
Security requires ongoing education from the whole team. Regular training ensures everyone understands their role in maintaining a secure ecosystem. Informed teams are more likely to build security into daily workflows.
Measure progress with practical API security metrics
You must measure performance over time to improve. Practical metrics, such as inventory coverage and the rate of remediation for identified vulnerabilities, reveal your security posture. These data points help leadership see the value of your API governance efforts.
| Maturity Level | Inventory Status | Policy Enforcement | Training Frequency |
|---|---|---|---|
| Initial | Manual spreadsheets | Ad-hoc | None |
| Defined | Automated discovery | Standardized | Annual |
| Optimized | Real-time tracking | Automated CI/CD | Continuous |
Prioritize API Security Improvements for Long-Term Protection
Transforming your security posture starts with a proactive, strategic roadmap instead of reactive fixes. Effective API security development requires a mindset focused on long-term resilience, not individual bug patches.
Start with identity, authorization, inventory, and exposure management
You cannot protect what you do not know exists. Build a complete inventory of every endpoint so your security team finds hidden assets.
After gaining visibility, focus on strengthening identity and authorization. Controlling user and service access helps prevent unauthorized entry to your data.
Rank vulnerabilities by business risk rather than technical severity alone
Not every vulnerability creates the same business threat. Assess each risk by data sensitivity and its potential effect on core business functions.
Using a business-first approach to API risk management directs limited resources toward your infrastructure’s most critical areas.
Automate repeatable controls without slowing responsible delivery
Security should not slow your engineering teams. Automating routine checks and policy enforcement maintains high standards while protecting development speed.
Choose tools that connect directly with your existing pipelines. Developers can catch issues early while focusing on delivering value to your customers.
Review security after major product, cloud, or integration changes
Your environment keeps changing, so your security strategy must keep pace. Review security after each major update or new third-party service connection.
This practice reveals new attack surfaces before attackers exploit them. Staying alert during change supports effective API security development.
Build a practical roadmap for continuous API risk reduction
Security success is a marathon, not a sprint. Set clear, measurable milestones that track progress as your business grows.
Effective API risk management requires ongoing commitment and refinement. A structured roadmap builds a security culture that protects your organization for years.
Conclusion
Building resilient software requires teams to rethink connectivity. Effective API security development combines strong architecture with constant checks across every infrastructure layer.
Your APIs connect customers, partners, and core business systems. API security development protects these paths through identity management, data encryption, and proactive traffic monitoring.
Begin by gaining full visibility into your existing endpoints. Prioritize access control and threat modeling to address risks before they affect users. This API security development approach shifts defense from reactive to predictive.
Reliable applications depend on adapting to new threats. Add automated testing and incident response planning to daily engineering workflows. These API security development practices help teams stay ahead of potential vulnerabilities while maintaining high performance.
Treat security as a core product lifecycle component, not an afterthought. A culture of shared responsibility protects sensitive information and preserves stakeholder trust. Consistent API security development creates a stable foundation for long-term business growth.