


Cloud computing moves fast, so protecting digital assets matters more than ever. As teams expand their platforms, strong SaaS security becomes harder to maintain and needs proactive care. Generic tools often leave gaps that attackers can exploit.
Custom vulnerability management software development helps teams find, rank, and fix application risks with precision. Solutions built around your cloud delivery practices can find threats faster and protect users more effectively.
This article explains the main needs for building these systems. We cover key integrations, architecture design, automated workflows, and compliance standards. You will also learn to simplify testing and planning, supporting a secure product lifecycle.
Table of Contents
Key Takeaways
- Custom security tools provide better visibility into unique cloud environments.
- Automated workflows help teams resolve critical risks with greater speed.
- Aligning security with delivery practices reduces friction for engineering teams.
- Compliance and testing are foundational elements of a secure architecture.
- Strategic planning ensures your protection scales alongside your user base.
Why SaaS Applications Need Purpose-Built Vulnerability Management
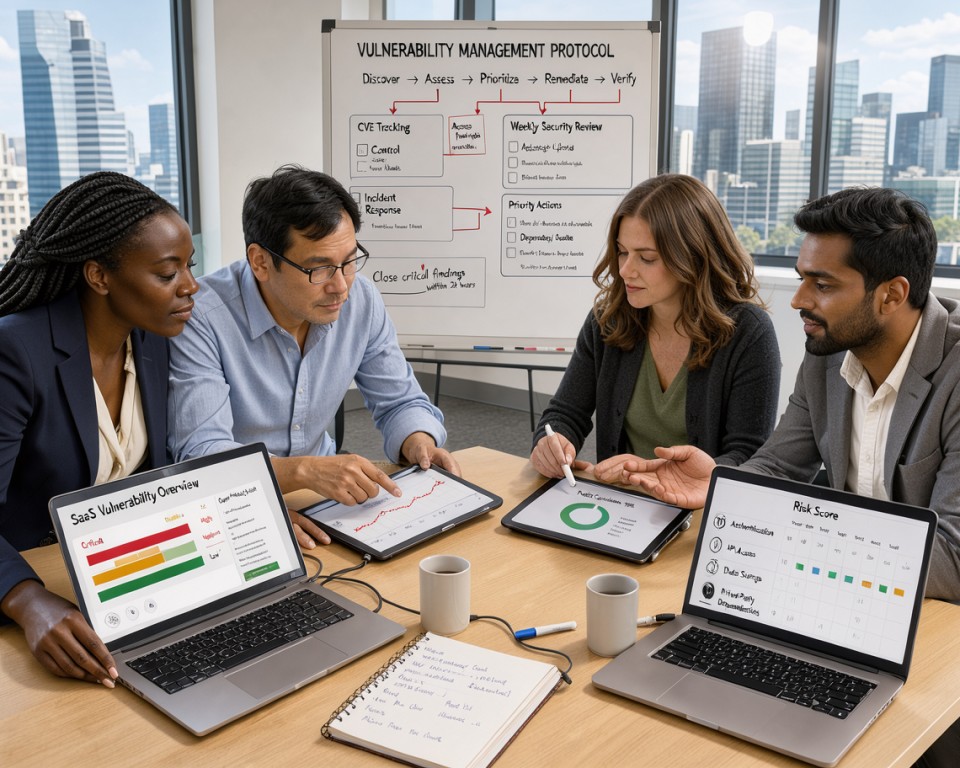
Modern SaaS platforms face a complex digital landscape that demands more than standard security tools. These applications change often and remain open to the public internet, so they need a specialized risk approach. Effective SaaS vulnerability management must reflect how these services are built, deployed, and used.
How Shared Infrastructure Expands the Attack Surface
Most SaaS products use shared infrastructure to improve efficiency and scale. This model supports business growth but creates serious security challenges. A single flaw in one shared component could expose data from several tenants.
Multi-tenancy is central to the SaaS model, but it also creates complex dependencies. If attackers bypass isolation layers, they could access sensitive customer information without permission. Therefore, strong SaaS security is essential for every engineering team.
Why Traditional Scanners Miss SaaS-Specific Risks
Many legacy security tools support static, on-premise environments. They often cannot keep up with rapid release cycles or modern cloud applications. These scanners often miss critical areas, such as:
- API endpoints that serve as the backbone of SaaS connectivity.
- Microservices that communicate across internal networks.
- Third-party integrations that introduce hidden supply chain risks.
Traditional scanners lack context, so they often create too much noise. Security teams then spend hours sorting false positives instead of fixing real threats. A purpose-built solution understands the business context of your code, so teams fix the most dangerous flaws first.
The Business Impact of Unresolved Vulnerabilities
“Security is not just a technical requirement; it is the foundation of customer trust in the digital economy.”
When a vulnerability remains unresolved, its effects go beyond technical debt. A breach can disrupt service, frustrate users, and harm your brand’s reputation. Failing to address these risks can also cause severe financial penalties and contract breaches.
Strong SaaS security supports long-term success. By investing in proactive SaaS vulnerability management, companies can protect assets and build customer confidence. Ultimately, a secure platform gives companies a competitive advantage in today’s crowded market.
Vulnerability Management Software Development: Goals and Core Outcomes
Building a strong security posture requires a clear vision for your vulnerability management software development. The main goal is replacing fragmented tools with one system that provides total visibility. Aligning technical goals with business objectives makes security a competitive advantage, not a bottleneck.
Centralizing Risk Discovery Across the SaaS Environment
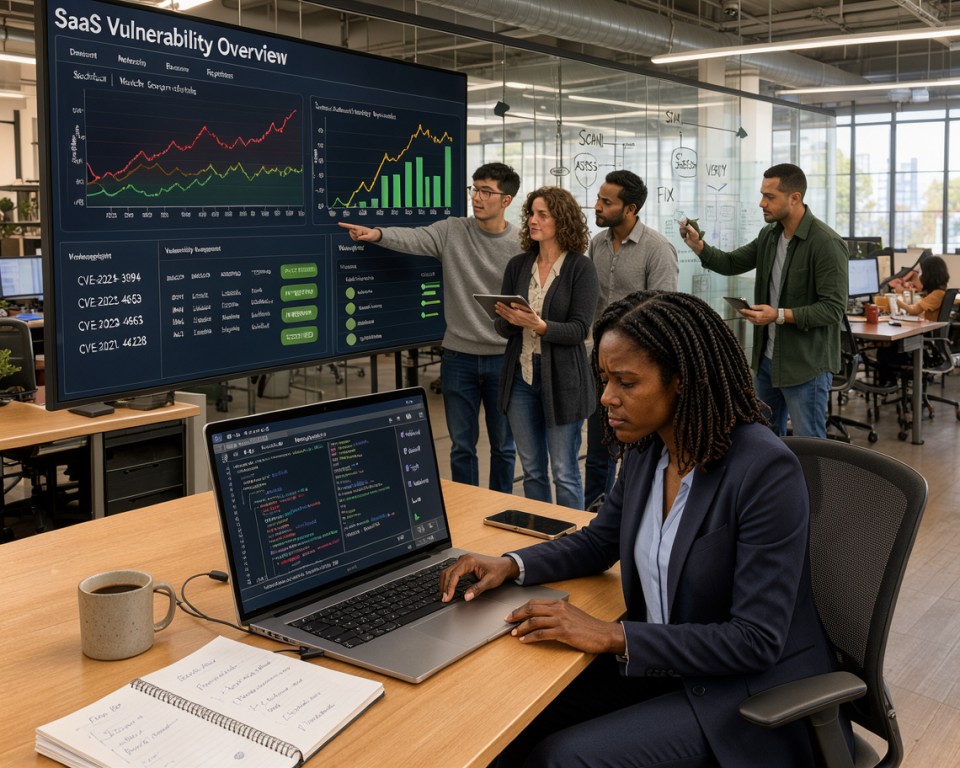
A modern vulnerability management platform must serve as one source of truth for all security data. Instead of switching between isolated scanners, teams need one dashboard that maps every asset. This visibility helps teams find coverage gaps before attackers exploit them.
Centralization also applies security policies consistently across the infrastructure. Unified discovery makes it easier to track assets, cloud resources, and API endpoints in real-time. This holistic view supports compliance and reduces the overall attack surface.
Turning Technical Findings Into Actionable Priorities
Raw technical data rarely drives effective remediation. A high-quality platform must turn complex scan results into actionable priorities developers can understand. Adding business context, such as customer impact and data sensitivity, helps teams focus on serious risks.
This process removes noise and false positives while highlighting critical vulnerabilities. Clear, context-rich reports help developers fix issues faster and with greater confidence. Prioritization connects finding a threat with successfully stopping it.
Supporting Continuous Security Without Slowing Product Delivery
The main goal of the vulnerability management lifecycle is integrating security into development. Security should not be a final gate that stops production. Instead, it should be an automated layer that runs alongside code changes.
This approach helps engineering teams move quickly while keeping applications secure. Embedding security checks into existing workflows reduces friction and builds shared responsibility. Developers with the right tools can address vulnerabilities early in development.
Defining Requirements for a SaaS Vulnerability Management Platform
Build your security foundation by defining clear requirements for your vulnerability management platform. The solution must meet United States SaaS needs while helping security teams and developers work well. Clear goals keep the platform effective and scalable as your business grows.
Security, Compliance, and Business Requirements
Modern SaaS companies must follow many regulatory standards. Your platform should support SOC 2, ISO 27001, and HIPAA from day one. These standards help build customer trust, not just meet technical demands.
Your business must also protect data and reduce risk. A strong strategy connects security results to business goals, so each scan and report delivers actionable value to stakeholders. This connection helps leaders support investment in security tools.

Functional Requirements for Security Teams and Developers
Security analysts need a vulnerability management platform that makes discovery and triage easier. They need clear dashboards that show critical risks without excess noise. Developers need tools that fit existing workflows, including IDE plugins and CI/CD pipeline hooks.
The goal is to reduce friction between these groups. Clear remediation guidance and automated ticketing help developers fix issues faster. This collaborative approach supports fast product delivery without weakening security.
Scalability, Availability, and Multitenancy Requirements
As your SaaS application grows, your security tools must keep up. High availability is essential because monitoring must run continuously against emerging threats. Also, multitenancy lets cloud-native security products serve customers efficiently while maintaining strict performance standards.
Tenant Isolation and Data Segmentation
Protecting customer data is the top priority in a shared environment. Strong tenant isolation ensures one customer’s findings never reach another customer’s account. Proper data segmentation supports a secure, multi-tenant architecture and blocks unauthorized platform access.
Role-Based Access and Administrative Boundaries
Effective security management requires precise control over who can see and do what. With role-based access control (RBAC), only authorized staff can change security policies or view sensitive vulnerability data. These boundaries prevent mistakes and protect security operations.
Designing the Vulnerability Discovery and Asset Inventory Layer
You cannot secure what you cannot see, so asset visibility anchors modern defense. A reliable asset inventory gives vulnerability scanning systems the context needed to identify protected assets. Without it, security teams struggle to rank risks.

Building a Complete Inventory of SaaS Assets
An effective inventory must cover more than simple server lists. It should show how components connect across your SaaS ecosystem. A real-time map helps organizations keep every infrastructure part under security oversight.
Discovering Applications, APIs, Containers, and Cloud Resources
Modern cloud security needs automated tools that can search different environments. These tools must find public-facing APIs, internal microservices, and containerized workloads. By polling cloud providers often, the system keeps the inventory accurate as environments change.
Tracking Asset Ownership, Environments, and Business Context
Knowing an asset exists is only half the battle; its purpose matters too. Ownership and business context help teams separate a low-risk staging server from a critical production database. This metadata helps vulnerability scanning produce useful results that support business goals.
| Asset Type | Security Risk Level | Primary Concern |
|---|---|---|
| Public APIs | High | Unauthorized access |
| Production Containers | Critical | Data exposure |
| Staging Environments | Medium | Configuration drift |
| Shadow Assets | High | Lack of oversight |
Handling Ephemeral Infrastructure and Short-Lived Assets
Many modern applications use ephemeral infrastructure that may exist for only a few minutes. Manual tracking often misses these assets before they disappear. Fast automated discovery logs these resources and adds temporary components to your asset inventory.
Detecting Unknown and Shadow Assets
Shadow IT remains a major challenge for cloud security teams. When developers launch resources outside standard workflows, they create blind spots attackers can exploit. Proactive scanning finds these unknown assets and brings them under security policy before they become liabilities.
Integrating Scanners and Security Testing Sources
A complete security strategy connects separate testing tools through one platform. Centralizing your security integrations gives you a broader view of risk than separate tools provide.
Combining SAST, DAST, and Software Composition Analysis
Modern development needs a layered approach to security testing. Combining Static Application Security Testing (SAST) with Dynamic Application Security Testing (DAST) finds flaws in source code and during runtime.
Software Composition Analysis (SCA) finds vulnerabilities in open-source libraries. Feeding all three sources into one workflow helps prevent critical bugs from escaping your development pipeline.
Adding Container, Infrastructure-as-Code, and Cloud Scanning
Your application is only as secure as its environment. Integrating cloud security tools helps monitor production for misconfigurations and unauthorized access points.
Scanning Infrastructure-as-Code (IaC) templates and container images prevents security gaps before deployment. This proactive approach helps harden your entire stack against modern threats.
Connecting Penetration Testing and Bug Bounty Findings
Automated tools are powerful, but they cannot replace creative human researchers. Connecting penetration testing reports and bug bounty program results to your central dashboard gives your team invaluable context.
This integration helps you compare automated findings with real-world exploit attempts. It also helps prioritize fixes based on what attackers target in your environment.
Normalizing Findings From Different Security Tools
Each scanner uses different terms, making vulnerability scanning hard to manage at scale. Normalization maps varied data formats into one consistent schema.
This step supports deduplication, so you avoid fixing the same issue reported by three different tools. A clean, normalized dataset forms the foundation of an efficient security workflow.
Managing Scanner Credentials and API Rate Limits
Reliable security integrations require careful control of authentication and throughput. Store scanner credentials securely to prevent unauthorized access to sensitive security data.
Respecting API rate limits helps maintain stable connections with external testing sources. Smart queuing and retry logic help your platform receive the latest security intelligence without interruption.
Creating Accurate Vulnerability Detection and Validation Workflows
Accurate vulnerability detection forms the foundation of any mature security program. Without reliable ways to verify findings, engineering teams may chase false alarms instead of fixing real risks. Structured validation workflows give each alert enough context for quick action.

Collecting Evidence for Each Security Finding
A strong security finding needs more than a severity score. It needs concrete evidence, including raw request payloads, stack traces, and specific response headers. This data helps developers reproduce the issue quickly without guessing its root cause.
When a scanner finds a possible flaw, the system should capture the application’s state at that moment. Evidence turns vague warnings into clear tasks. It helps developers see why the code is risky.
Reducing False Positives Through Deduplication and Verification
Effective vulnerability detection needs a deduplication engine that groups similar issues across environments. Security teams often face alert fatigue from repeated or inaccurate findings. Merging identical findings gives developers one consolidated ticket for each recurring problem.
“The true measure of a security program is not how many vulnerabilities you find, but how quickly you can distinguish the signal from the noise.”
Verification is the next step in cleaning up your security backlog. Automated scripts can try to trigger a finding again in a sandbox environment. If the scanner cannot reproduce the issue, the system should downgrade or suppress the alert automatically.
Detecting Vulnerabilities in APIs and Authentication Flows
Modern SaaS platforms depend on complex API interactions and authentication handshakes. Attackers often target these areas, making them a priority for automated testing. A strong platform must understand authentication logic, not just simple code patterns.
Testing Authorization and Tenant-Isolation Controls
In a multi-tenant environment, tenant isolation is the key security boundary. If one user accesses another user’s data, the SaaS application’s trust model collapses. Automated tests must target authorization headers and session tokens, ensuring data stays siloed.
Validating Business-Logic and Configuration Vulnerabilities
Beyond standard exploits, business-logic flaws often hide in plain sight. These flaws occur when an application works as designed but permits an unintended outcome, such as bypassing a payment step. Proper validation means testing configuration settings against known security benchmarks to prevent common misconfigurations.
| Validation Method | Primary Benefit | Complexity Level |
|---|---|---|
| Automated Deduplication | Reduces Alert Fatigue | Low |
| Payload Reproduction | Speeds Up Remediation | Medium |
| Tenant Isolation Testing | Prevents Data Leaks | High |
| Configuration Auditing | Ensures Compliance | Medium |
Prioritizing SaaS Vulnerabilities by Exploitability and Business Risk
Effective risk prioritization keeps a SaaS platform secure without exhausting developers. When security tools create hundreds of alerts, teams can feel overwhelmed by the amount of data. By focusing on what matters most, your team can protect the business and keep product delivery on track.

Using Severity Scores Without Relying on Them Alone
Standard severity scores offer a useful starting point, but they rarely show the full risk. A high-severity finding on an isolated server may pose less danger than a medium-severity flaw on public login pages. Context is everything when securing a complex application.
Relying only on automated scores can waste effort on low-risk items. Treat these scores as one piece of a larger puzzle. This balanced approach keeps your SaaS vulnerability management strategy grounded in reality.
Combining CVSS, Exploit Intelligence, and Exposure Data
To make better decisions, you must combine technical metrics like CVSS with real-world threat intelligence. Knowing that a vulnerability is actively being exploited in the wild changes the urgency of the fix immediately. You should also consider whether the affected component is exposed to the internet or hidden behind multiple security layers.
By layering exposure data over technical findings, you can filter out noise. This lets your security team focus on vulnerabilities that pose a genuine threat to your infrastructure. Smart prioritization turns raw data into a clear roadmap for your engineering department.
Adding Asset Criticality and Customer Impact to Risk Decisions
Not every asset in your environment carries equal weight. You must assess how a potential breach could affect customers and core business operations. A vulnerability in a payment processing module is more critical than one in a non-production marketing site.
Prioritizing Internet-Facing Production Services
For teams serving the United States market, internet-facing production services are the highest priority. These systems are highly visible and likely targets for malicious actors. Quick action here is essential to maintain customer trust and platform integrity.
Separating Compliance Findings From Urgent Exploitation Risks
You must distinguish compliance requirements from immediate exploitation risks. Meeting SOC 2 or HIPAA standards is necessary, but some findings may not signal an active security threat. Manage these as separate workstreams so urgent, high-risk vulnerabilities are not delayed by administrative paperwork.
Building Remediation Workflows That Developers Can Use
You can strengthen your security posture by adding actionable vulnerability remediation to tools developers already use. Isolated security reports often get ignored or buried in backlogs. A workflow that speaks to engineers makes security part of the development lifecycle.
Assigning Findings to the Correct Engineering Owners
The first step is sending every finding to the right person at once. Automated routing should map vulnerabilities to teams using code ownership, service metadata, or cloud resource tags. This removes the friction of manual triage and keeps alerts out of generic inboxes.
Providing Reproduction Steps, Fix Guidance, and Context
Developers need more than a list of CVEs. Clear reproduction steps and code-level fix guidance help teams understand risk without a security degree. Context is everything; showing the affected asset, business criticality, and potential impact helps engineers set priorities.
Supporting Tickets, Pull Requests, and Collaborative Triage
Collaboration works best when security data stays where the work happens. Letting developers create tickets or pull requests from the security platform reduces context switching. This approach helps security and engineering teams solve issues together instead of pointing fingers.
Integrating Jira, GitHub, GitLab, and Slack
Strong security integrations support a modern remediation strategy. Connecting your platform to Jira, GitHub, GitLab, and Slack sends real-time notifications and creates trackable tasks. These integrations keep everyone aligned, so critical vulnerabilities do not slip through during a busy sprint.
Tracking Exceptions, Compensating Controls, and Risk Acceptance
Not every vulnerability can be fixed immediately, and that is okay. A mature workflow should track exceptions, document compensating controls, and manage risk acceptance. Transparent, auditable decisions clarify your security posture while helping developers ship features safely.
Automating Continuous Vulnerability Management in CI/CD
Putting security in the pipeline changes how teams manage vulnerabilities. With CI/CD security in the development lifecycle, organizations can find risks before they reach users. This approach makes security a continuous engineering task, not a final hurdle.
Scanning Code and Dependencies Before Deployment
Automated scans check source code and third-party libraries first. During the commit phase, developers get quick feedback about flaws, including hardcoded secrets and outdated dependencies. This early detection lowers the cost and effort of fixing issues later.
Setting Risk-Based Build and Release Gates
Not every vulnerability needs an immediate production halt. With security automation, teams can set risk-based gates that block deployments only for critical or high-severity threats. This balance tracks minor issues without slowing the release cycle.
Monitoring Production Changes After Release
Security work continues after code reaches the cloud. Continuous monitoring tracks infrastructure changes and application behavior for drift or new post-release vulnerabilities. This visibility supports modern DevSecOps and gives teams data to respond to threats in real time.
Preventing Automation From Creating Alert Fatigue
Too many notifications can overwhelm developers and cause important warnings to be ignored. Intelligent filtering groups related findings and prioritizes the greatest business risks. As the saying goes:
“Security is not about stopping everything; it is about managing risk so that innovation can thrive safely.”
Designing Safe Rollbacks and Approval Paths
When production reveals a critical vulnerability, teams need a clear path to safety. Automated CI/CD security workflows should include pre-defined rollback procedures for an instant return to a known secure state. Clear approval paths for security exceptions keep human oversight central to the DevSecOps strategy.
Protecting Vulnerability Data and Platform Access
Your vulnerability management platform needs protection as strong as the applications it monitors. If attackers compromise your tools, your vulnerability data protection strategy could fail. Treat the platform as a high-value target and defend it with strict security controls.
Encrypting Findings, Credentials, and Security Evidence
Protect all platform data at rest and in transit. This includes security findings, raw scan results, and credentials for accessing cloud environments. Encryption is not optional; it protects the integrity of your security operations.
Industry-standard encryption keeps stolen data unreadable, even after a breach. This protection supports SaaS security and helps you meet regulatory requirements.
Implementing Least-Privilege Access With Role-Based Controls
Give users only the permissions needed for their jobs. With Role-Based Access Control (RBAC), you can separate duties among analysts, developers, and administrators.
- Security Analysts: Access to view and triage findings.
- Developers: Access to remediation guidance and ticket status.
- Administrators: Full control over system configuration and user management.
Maintaining Audit Trails for Administrative and Remediation Actions
A tamper-resistant audit trail supports accountability. Log every platform action, from changing settings to marking a vulnerability resolved. These records help investigate insider threats and answer auditor requests.
Using Secrets Management for Scanner Integrations
Never hardcode scanner or API integration credentials. Use a dedicated secrets management service to inject keys when needed. This reduces credential leaks and makes sensitive access tokens easier to rotate.
Applying Single Sign-On and Multifactor Authentication
Strong authentication provides the first defense for your platform. Integrating Single Sign-On (SSO) lets your team manage access through your existing identity provider. Enforcing Multifactor Authentication (MFA) adds protection against unauthorized access attempts.
Together, these safeguards greatly reduce the risk of unauthorized entry. This proactive approach to SaaS security builds customer confidence and keeps security operations resilient against changing threats.
Supporting Compliance and Security Reporting for SaaS Companies
Effective compliance reporting connects technical security work with business trust. Finding bugs matters, but clear reports help auditors and stakeholders understand your risks. This connection keeps your security program transparent and defensible.
Mapping Findings to SOC 2, ISO 27001, PCI DSS, and HIPAA Controls
Modern SaaS platforms must match security data to specific regulatory frameworks. You can map each vulnerability to controls in SOC 2, ISO 27001, PCI DSS, and HIPAA. This mapping provides clear evidence that your team manages risks affecting data privacy or system availability.
Automating this connection removes guesswork from your vulnerability management lifecycle. It shows that each identified risk links to a specific business control. This detail helps prove to regulators that your security measures work and remain active.
Generating Reports for Security Teams, Executives, and Auditors
Stakeholders need different views of your security data. Security teams need technical details for vulnerability remediation, while executives prefer high-level risk summaries. Auditors seek consistent records showing that your processes work reliably.
Customized dashboards show each audience the information it needs. Tailored reporting reduces explanations and gives your team more time to act. This efficiency reflects a mature security organization.
Measuring Remediation SLAs and Vulnerability Trends
Tracking resolution speed is a key metric for every SaaS company. Setting and monitoring vulnerability remediation SLAs keeps critical risks from lingering in your environment. These metrics show your team’s responsiveness and operational health.
Trend reports reveal recurring issues in your development pipeline. Analyzing these patterns improves your vulnerability management lifecycle and prevents future vulnerabilities from reaching production. This proactive approach turns raw data into useful business intelligence.
Preparing Evidence for Customer Security Reviews
In the United States, enterprise customers often require detailed security assessments before signing contracts. A clean, automated report on your current security status can speed up the sales cycle. Transparency during these reviews builds long-term trust and shows your commitment to protecting customer data.
Maintaining Historical Records for Audit Readiness
Auditors need proof that your security controls worked correctly over time. Keep historical records of findings, remediation actions, and policy changes for audit readiness. This practice prepares you for annual reviews without a last-minute search for documents.
Designing the Platform Architecture for Scale and Reliability
When you build a modern security tool, its architecture shapes long-term success. A vulnerability management platform must manage massive data streams and stay available for every user. Modular design keeps the system flexible as your customer base grows.
Choosing Services for Ingestion, Processing, and Storage
Effective ingestion needs a separate process for different security data formats. Use managed cloud services with elastic scaling to handle sudden spikes in scan activity. A hybrid strategy uses fast databases for active findings and low-cost object storage for historical logs.
Using Queues and Workers for High-Volume Scan Results
A strong message queue helps prevent system bottlenecks. Distributed workers let your vulnerability management platform process thousands of findings in parallel without slowing the user interface. This asynchronous model maintains consistent performance during peak scanning hours.
Planning for Regional Hosting and Data Residency
Global SaaS companies must follow complex data sovereignty laws. Architectural multitenancy isolates customer data within specific geographic regions. This approach meets compliance needs and improves speed for international users.
Managing Rate Limits and Backpressure
Your system must handle data surges without service degradation. Smart rate limits stop one tenant from using too many resources. When capacity is reached, backpressure mechanisms tell upstream services to slow down and protect core infrastructure.
Designing Disaster Recovery and Business Continuity
Reliable systems assume that failures will occur. Design your multitenancy environment with automatic failover across multiple availability zones. Regular backups and a clear recovery roadmap protect customer trust and prevent prolonged downtime for security operations.
Your platform succeeds when it balances performance with security. A scalable architecture gives users a stable foundation for managing risks effectively. A well-designed system supports multitenancy while keeping operating costs predictable and manageable.
Testing and Validating the Vulnerability Management Product
You cannot claim to protect SaaS environments until you test your own platform. Before production, it must pass rigorous validation to ensure vulnerability detection stays accurate and reliable. This process builds trust in software used for daily security operations.
Testing Detection Accuracy With Known Vulnerable Applications
To verify your engine, deploy intentionally vulnerable applications, such as OWASP Juice Shop or WebGoat. These controlled environments provide a baseline for measuring how well your scanner finds common flaws. Consistency is key when checking for false positives and false negatives.
Performing Security Testing Against the Platform Itself
Your platform is a high-value target, so it needs its own security testing. Run regular penetration tests and automated red-team exercises to find weaknesses in your architecture. A flaw could become the entry point attackers use to compromise customers.
Validating Integrations, Permissions, and Tenant Isolation
SaaS platforms rely on complex connections to cloud providers and CI/CD pipelines. Verify that every integration follows the principle of least privilege. Strict tenant isolation must ensure one customer’s data never leaks into another’s environment during a scan.
Measuring Scan Performance and Result Processing Time
Security teams need timely data to make informed decisions. Benchmark the time needed to complete a full scan and process its findings. If latency is too high, developers may ignore feedback, making the tool ineffective.
Testing Failure Recovery for External Security Tools
External scanners and APIs will sometimes fail or time out. Your platform must handle these interruptions without crashing or losing data. Use retry logic and clear error reports so users know when manual intervention is needed.
| Validation Metric | Target Goal | Testing Method |
|---|---|---|
| Detection Accuracy | >95% True Positives | Known Vulnerable Apps |
| Tenant Isolation | Zero Cross-Leakage | Automated Penetration Tests |
| Scan Latency | Under 30 Minutes | Performance Benchmarking |
| Recovery Rate | 100% Graceful Failover | Simulated API Outages |
Planning Development Costs, Timelines, and Team Responsibilities
A successful security tool launch depends on balancing development costs with long-term goals. A clear plan keeps your vulnerability management software development focused on real value for your organization.
Estimating Work Across Discovery, Automation, and Reporting
Accurate estimates start by dividing the project into manageable modules. Allow time to build asset discovery engines, connect scanners, and create clear reporting dashboards.
- Asset Discovery: Requires significant backend effort to map cloud resources and APIs.
- Security Automation: Involves building workflows that trigger scans and handle data ingestion.
- Reporting: Focuses on creating actionable insights for stakeholders and auditors.
Choosing Between Custom Development and Commercial Components
Choosing between building from scratch and buying components is a key strategic decision. Custom solutions provide full control, while commercial components can speed up time-to-market.
| Factor | Custom Build | Commercial Components |
|---|---|---|
| Integration | High effort | Low effort |
| Ownership | Full control | Vendor dependent |
| Scalability | Highly flexible | Limited by vendor |
Assigning Responsibilities to Security, Product, and Engineering Teams
Clear ownership prevents bottlenecks and helps embed DevSecOps principles into your culture. Security teams define requirements, while product managers rank features by business risk.
Engineering teams handle the platform’s technical build and maintenance. This shared model makes security automation a team goal, not a siloed task.
Planning an MVP With High-Value Security Capabilities
Start with an MVP that tackles the most critical risks first. Prioritize automated asset inventory and basic vulnerability scanning for immediate team visibility.
A working MVP lets you collect feedback early and improve your approach. This cycle helps maintain momentum in your vulnerability management software development journey.
Expanding the Roadmap With Threat Intelligence and Automation
After the foundation is stable, add advanced features. Threat intelligence helps your team rank vulnerabilities using real-world exploit data, not severity scores alone.
More investment in DevSecOps workflows can connect your platform more deeply with CI/CD pipelines. This growth helps your security automation keep pace with infrastructure and protect SaaS applications as they scale.
Conclusion
Protecting modern digital services requires proactive defense strategies. A purpose-built vulnerability management lifecycle helps your team discover, validate, and fix risks with precision. This approach keeps security aligned with rapid software delivery cycles.
Effective SaaS vulnerability management needs more than automated scanning tools. It combines developer-friendly workflows, strong architecture, and continuous testing. Clear context and fix guidance help developers resolve issues without disrupting the product roadmap.
Your organization should prioritize a roadmap that matches customer expectations and United States market standards. Map your unique environment to these core security principles. This path strengthens protection for applications and the users who rely on them every day.
Evaluate your current security posture against these requirements. Building a tailored platform today creates a safer foundation for your business tomorrow. Your commitment to these practices will shape your security program’s long-term success.